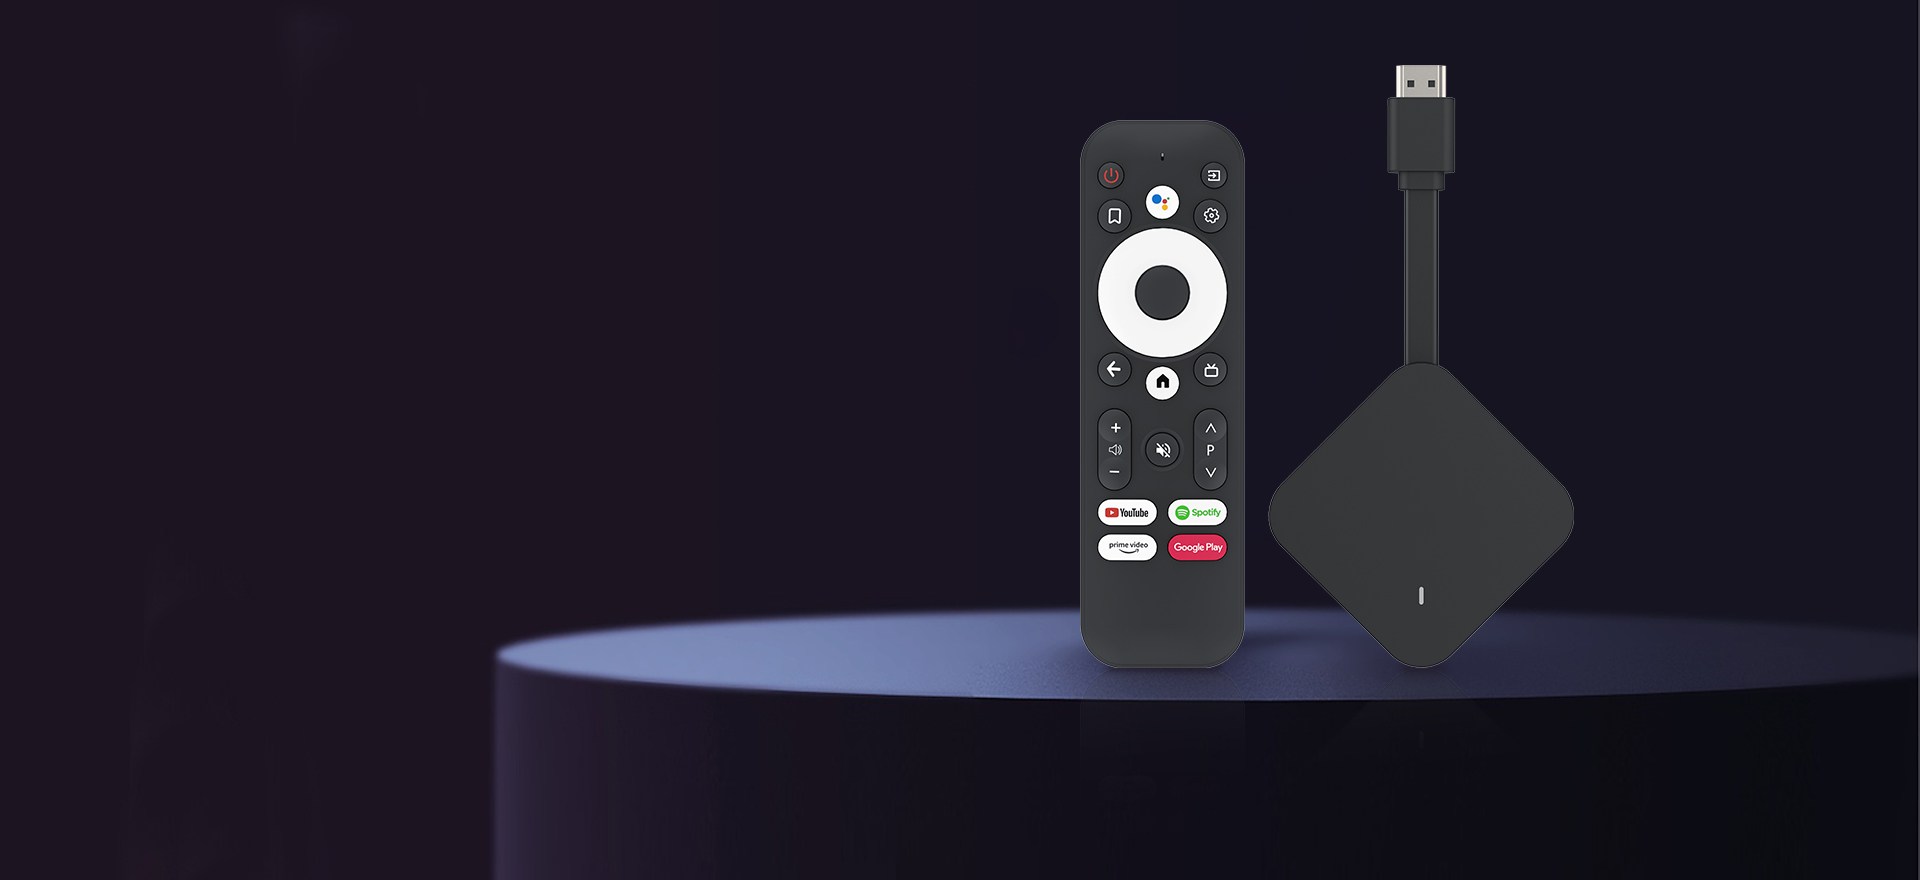
Google says a manufacturer ‘intentionally’ hijacked its devices with malware.Google says a manufacturer ‘intentionally’ hijacked its devices with malware.Nov 2, 2026, 8:37 PM UTCA current Videostrong Android TV device. Image: VideostrongGoogle says one of its Android manufacturing partners secretly built a backdoor in 1.3 million devices and turned them into a botnet. The company says it has now dismantled the backdoor and “cut ties” with the manufacturer, the Shenzhen, China-based Videostrong Technology Co., which has been banned from building or selling certified Android devices or supplying software for them.The infected devices were used without owners’ knowledge for “malicious activity,” like ad fraud, data exfiltration, and routing unauthorized network traffic. Google claims the “backdoor and botnet were intentionally developed, deployed, and operated for financial gain,” saying:Videostrong monetized the backdoor by selling access to criminal affiliates and loading those affiliates’ malware modules onto infected devices. These secondary modules were conducting ad-fraud; silently enrolling infected devices into residential proxy networks; and loading additional malware onto XCPE-compromised devices. We also took action to disrupt the command and control (C2) domains that operate these affiliate modules. Because these affiliates each have diversified distribution channels for their modules beyond XCPE, we assess that taking down their C2 domains will sever access to at least 10 million additional compromised devices.RelatedIt wasn’t just one device that was impacted, either — the malware was found “built directly into many different device models and brands over multiple years.” Most of those were Android TV set-top boxes, but the botnet also infected other “Android-based IoT devices, including telehealth devices, karaoke machines, and digital signage devices.”Google says Videostrong used “obfuscation techniques” to load the malware onto users’ devices after they booted up the hardware for the first time. Google also says it made changes to its review process for device manufacturers after this incident.Follow topics and authors from this story to see more like this in your personalized homepage feed and to receive email updates.Stevie BonifieldThe Verge DailyA free daily digest of the news that matters most.Email (required)By providing your information, you agree to our Terms of Use and our Privacy Policy. We use vendors that may also process your information to help provide our services. This site is protected by reCAPTCHA and the Google Privacy Policy and Terms of Service apply.
One of Google’s Android partners turned 1.3 million set-top boxes into a botnet